Search Application event that contains a specific word in the message event.
get-eventlog Application | where-object {$_.Message -Contains 'MSXML'} | select -first 1 | FL
I have also tried the -match but no outcome.
Search Application event that contains a specific word in the message event.
get-eventlog Application | where-object {$_.Message -Contains 'MSXML'} | select -first 1 | FL
I have also tried the -match but no outcome.
-contains is for checking if an array contains an object. As you correctly suggest, you should be using the -match operator. Changing your code to use -match worked OK for me.
Get-EventLog Application | Where-Object {$_.Message -Match 'MSMXL'} |
    Select-Object -first 1
However, Get-EventLog is deprecated, so perhaps you’ll have more luck with Get-WinEvent
Get-WinEvent -LogName Application | Where-Object {$_.Message -match 'MSXML'} |
    Select-Object -First 1
Okay. It works. Thank you so much Matt!
So that means -match operator allows the script to just find that word in the message of the event.
But -contain fails because it is not an array.
Just want to understand the difference.
-match looks for a regular expression (regex) pattern in a string.
-contains checks if a collection, such as an array, contains a value.
PS E:\Temp> 'I am a string' -contains 'string'
False
PS E:\Temp> 'I am a string' -match 'string'
True
PS E:\Temp> @('I','am','an','array') -contains 'array'
True
See Get-Help about_Comparison_Operators for more information.
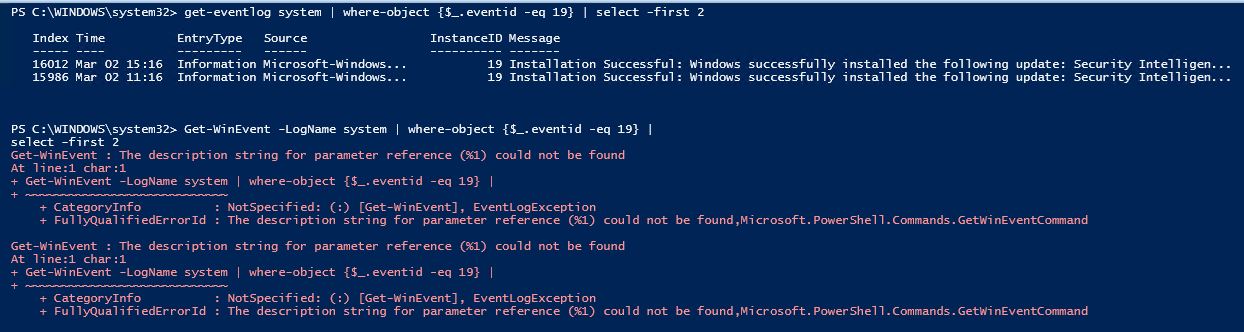
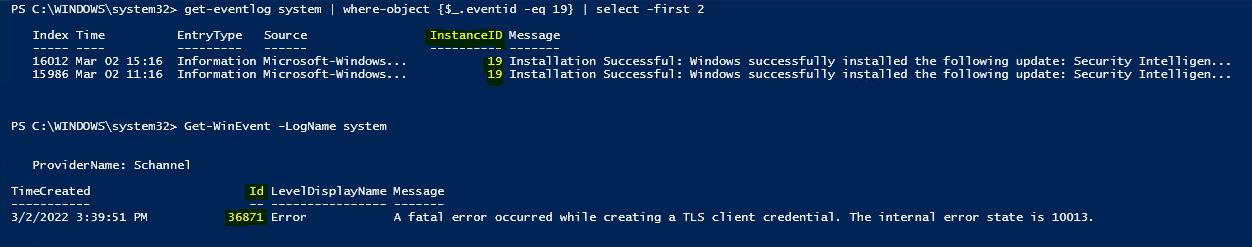
Does it work for a different Event ID?
I’ve not seen that error but from a quick search, it can occur if the event message contains ‘%% followed by a long number’.
You should also look at the help for Get-WinEvent and use a filter hashtable, rather than getting all the events then passing them to Where-Object.
Simple and well understandable. Thank you Matt!
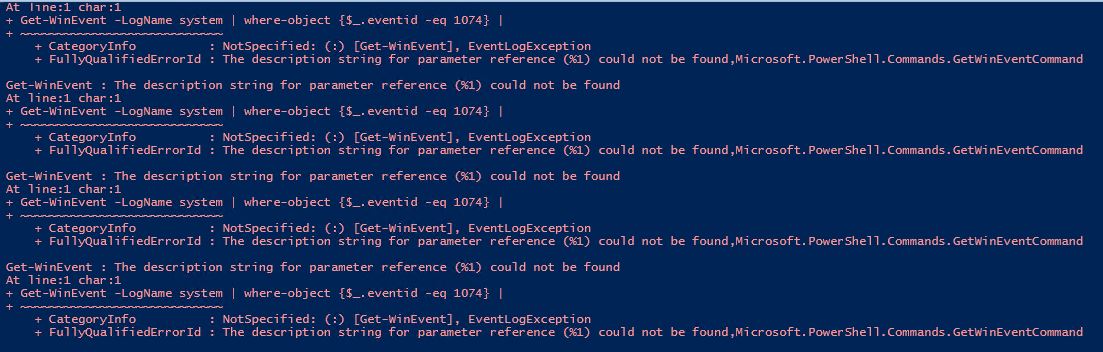
Please, when posting code and error messages, copy and paste the text, using the </> button. Images are not, in most cases, very helpful.
What operating system are you running this on, and what is the output of $PSVersionTable?
I am using Windows 10 version 21H2.

Ok, same version here and it’s working fine for me.
I think I would backup (if required) and then clear the event log and see if that resolves the problem.
Okay, I see. I will stick on the deprecated version then until the new version works for me.
Thank you Matt looking into this.
FWIW, I get results along with the same error, but I used:
Get-WinEvent -LogName 'System' | Where-Object {$_.ID -eq 1074}
Very odd …
This works now 
Get-WinEvent -LogName 'System' | Where-Object {$_.ID -eq 1074}


   ProviderName: User32

TimeCreated                      Id LevelDisplayName Message
-----------                      -- ---------------- -------
2/10/2022 6:27:20 PM           1074 Information      The process C:\Windows\System32\RuntimeBroker.exe (DESKTOP-JTQHNDS) has initiated the pow...
2/8/2022 12:00:02 AM           1074 Information      The process C:\WINDOWS\system32\svchost.exe (DESKTOP-JTQHNDS) has initiated the restart o...
1/24/2022 11:58:02 PM          1074 Information      The process C:\WINDOWS\system32\svchost.exe (DESKTOP-JTQHNDS) has initiated the restart o...
12/16/2021 2:56:58 PM          1074 Information      The process C:\WINDOWS\system32\winlogon.exe (DESKTOP-JTQHNDS) has initiated the shutdown...
12/16/2021 2:55:00 PM          1074 Information      The process C:\Windows\System32\RuntimeBroker.exe (DESKTOP-JTQHNDS) has initiated the res...
12/9/2021 8:13:13 PM           1074 Information      The process C:\Program Files\VMware\VMware Tools\vmtoolsd.exe (DESKTOP-JTQHNDS) has initi...
12/8/2021 5:29:52 PM           1074 Information      The process C:\WINDOWS\system32\winlogon.exe (DESKTOP-JTQHNDS) has initiated the restart ...
Thank you Tonyd!!!
Hmmm … I just get the expected output with:
$FilterHashTable = @{
    LogName = 'System'
    ID      = 1074
}

Get-WinEvent -FilterHashtable $FilterHashTable